> For the complete documentation index, see [llms.txt](https://glyue.docs.sandboxbanking.com/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://glyue.docs.sandboxbanking.com/how-to-guides/how-to-set-up-single-sign-on-sso/azure-setup.md).
# Azure Setup
{% hint style="warning" %}
Before continuing, this user should be an Azure AD admin for the organization, and a SAML Config must be created in the Integration Gateway Environment.
{% endhint %}
### Create the Integration Gateway Enterprise Application
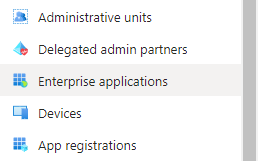
From the Azure Active Directory overview page, select **Enterprise applications** from the left-hand panel.
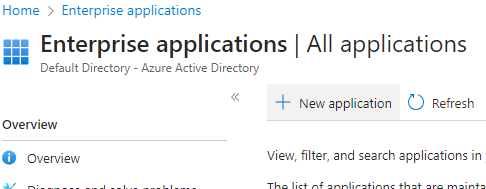
Click **New Application** at the top.
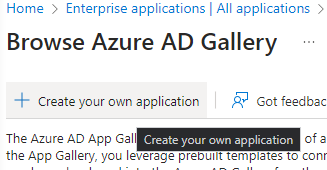
Click **Create your own application** at the top.
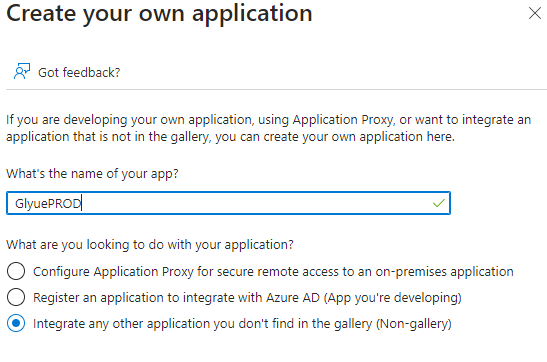
Provide a name and select **Integrate any other application you don’t find in the gallery (Non-gallery)**. Click **Create** at the bottom of the page.
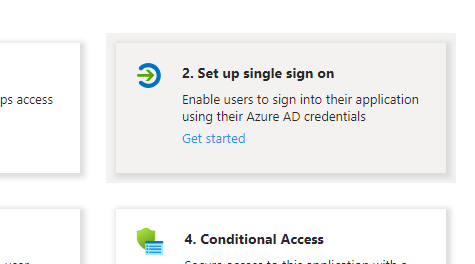
Click **2. Set up single sign on** under **Getting Started**, or select **Single sign-on** from the left-hand panel.
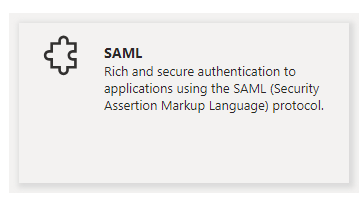
Select **SAML**.
### Provide Integration Gateway's metadata to Azure
{% hint style="info" %}
The Integration Gateway environment SAML metadata will be required for the next step.
Integration Gateway always serves its metadata at `https://` (custom domain) `/sso/saml2/metadata/`. If this user is also a Integration Gateway administrator, the metadata URL will be displayed on the **Admin** site under **SAML Configs**.
{% endhint %}
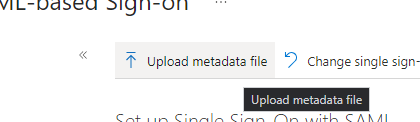
At the top, select **Upload metadata file.** Select the appropriate file and upload.
Click **Save** at the top.
### Add an email claim
We need to add a claim to the SAML configuration in Azure, so that the user’s email address comes over to Integration Gateway in a field titled “email” instead of something else.
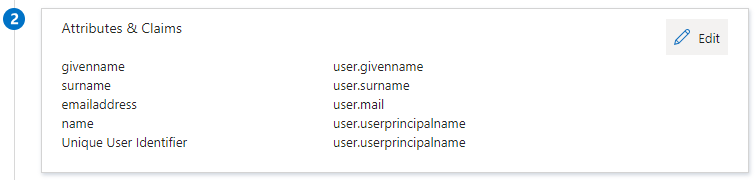
On the application **SAML-based Sign-on** page, in section **2 Attributes & Claims** click **Edit**.
Click **Add new claim** at the top.
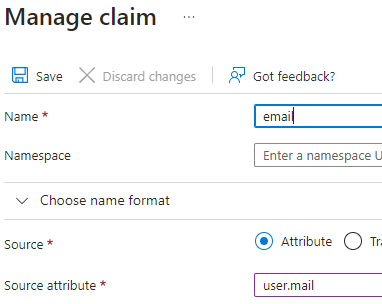
Enter `email` in the **Name** field. For **Source Attribute** select `user.mail`. Click **Save** in the top-left.
Depending on the organization’s Azure configuration, the user email field name may differ.
### Get Azure SAML metadata for Integration Gateway
On the application **SAML-based Sign-on** page, in section **3** under **SAML Certificates** download the **Federation Metadata XML**.
Alternatively, grab the **App Federation Metadata Url** instead of downloading the file.
This will be needed on the Integration Gateway side, to add Azure as an IdP. If this user is not a Integration Gateway admin, please provide the file/URL to a Sandbox Banking employee.
{% hint style="warning" %}
#### Lastly…
Don’t forget to assign users or groups to the new application- otherwise they won’t be able to authenticate with Integration Gateway via SSO.
{% endhint %}
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://glyue.docs.sandboxbanking.com/how-to-guides/how-to-set-up-single-sign-on-sso/azure-setup.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.